Digital Forensics & Investigations
Digital evidence examination and forensic investigation for legal and corporate matters.
Digital evidence may exist across devices, infrastructure, cloud environments, communications and multimedia content. Our forensic capabilities are structured to identify, preserve and examine relevant digital information based on the circumstances and scope of the matter.
Engagement Standards
Court-Admissible Chain of Custody
Bitstream imaging adhering strictly to ISO/IEC 27037 & statutory requirements.
Strict Non-Disclosure Protection
Confidential handling under full NDA & attorney-client privilege protocols.
Rapid Crisis Response SLA
Specialized digital forensic examiners deployed on-site or remote within hours.
Core Forensic Capabilities
Endpoint & Bit-Stream Disk Examination
Forensic examination of computers, servers and storage media to recover digital evidence, analyse user and system activity, identify data transfers and reconstruct events relevant to cyber incidents, misconduct and legal investigations.
Primary Investigation Vectors:
Endpoint & Bit-Stream Disk Examination
Forensic examination of computers, servers and storage media to recover digital evidence, analyse user and system activity, identify data transfers and reconstruct events relevant to cyber incidents, misconduct and legal investigations.
Primary Investigation Vectors:
What the Investigation May Establish
Whether relevant files existed
Whether information was accessed
Whether files were copied, move or deleted
Whether external storage was used
Whether information was transferred
Whether particular accounts or devices were involved
The timing of relevant communication
Relevant communications between parties
Whether deletion or concealment activity occurred
Relationships between evidence identified across systems
Related Insights
View all insights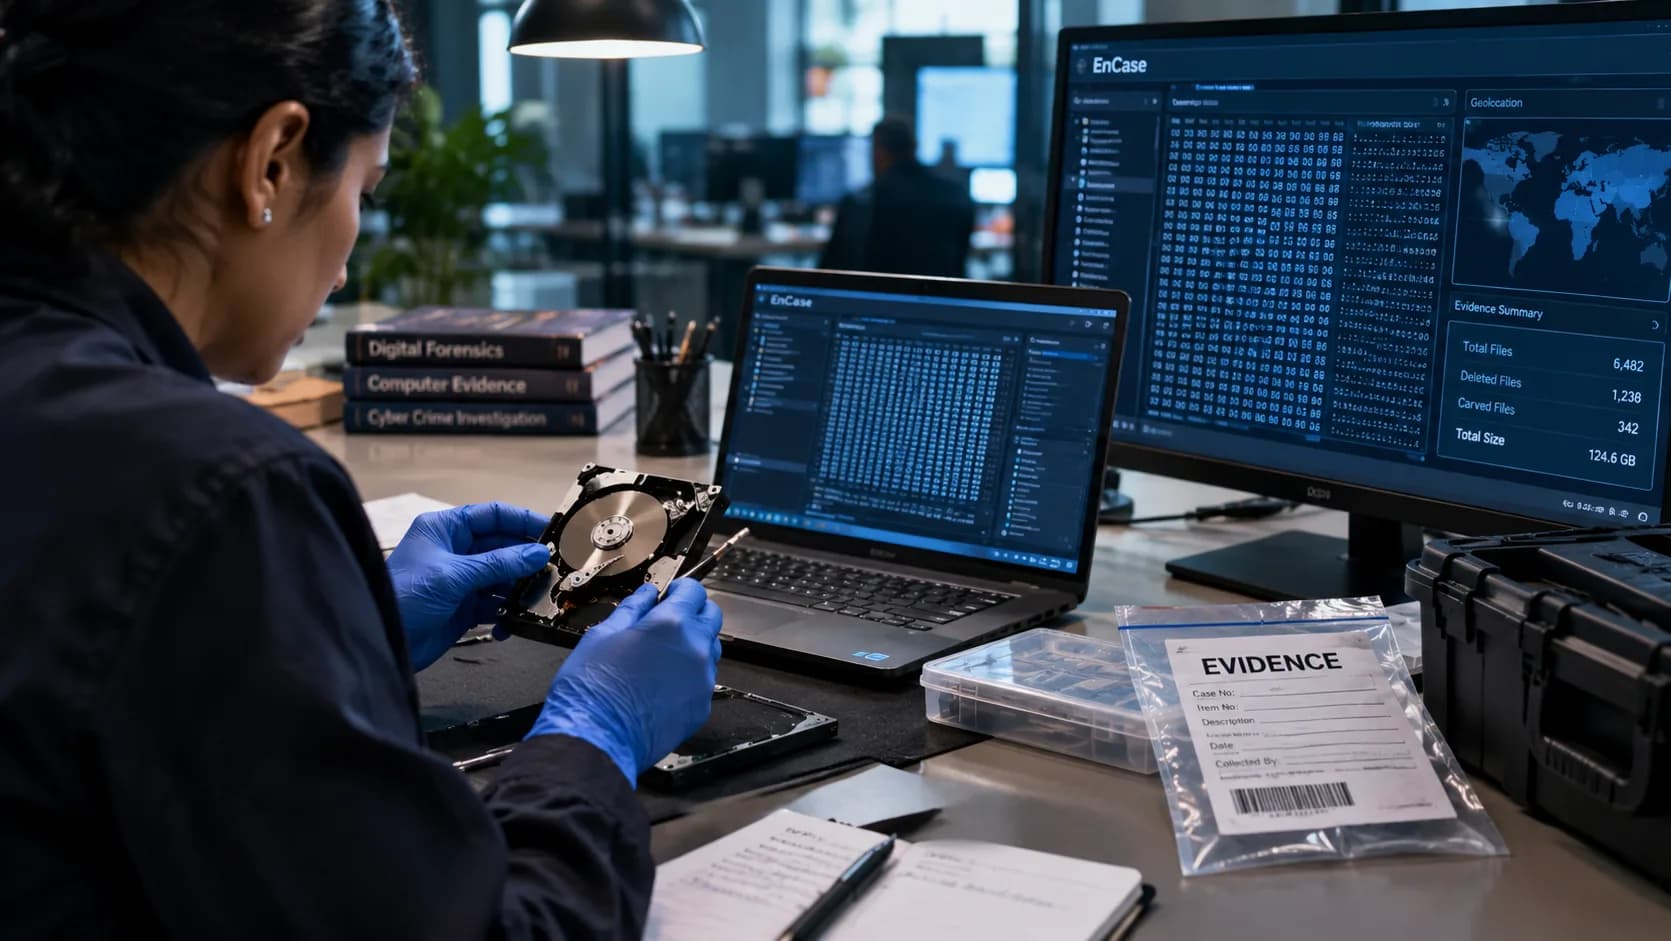
The Next Generation of Global Digital Forensic Discovery
As enterprise infrastructure disperses across multi-cloud regions, hybrid data centers, and encrypted endpoints, digital forensics requires unprecedented discipline. This research explores modern bit-stream imaging protocols, cryptographic integrity verification, and legal defensibility under updated evidentiary frameworks.
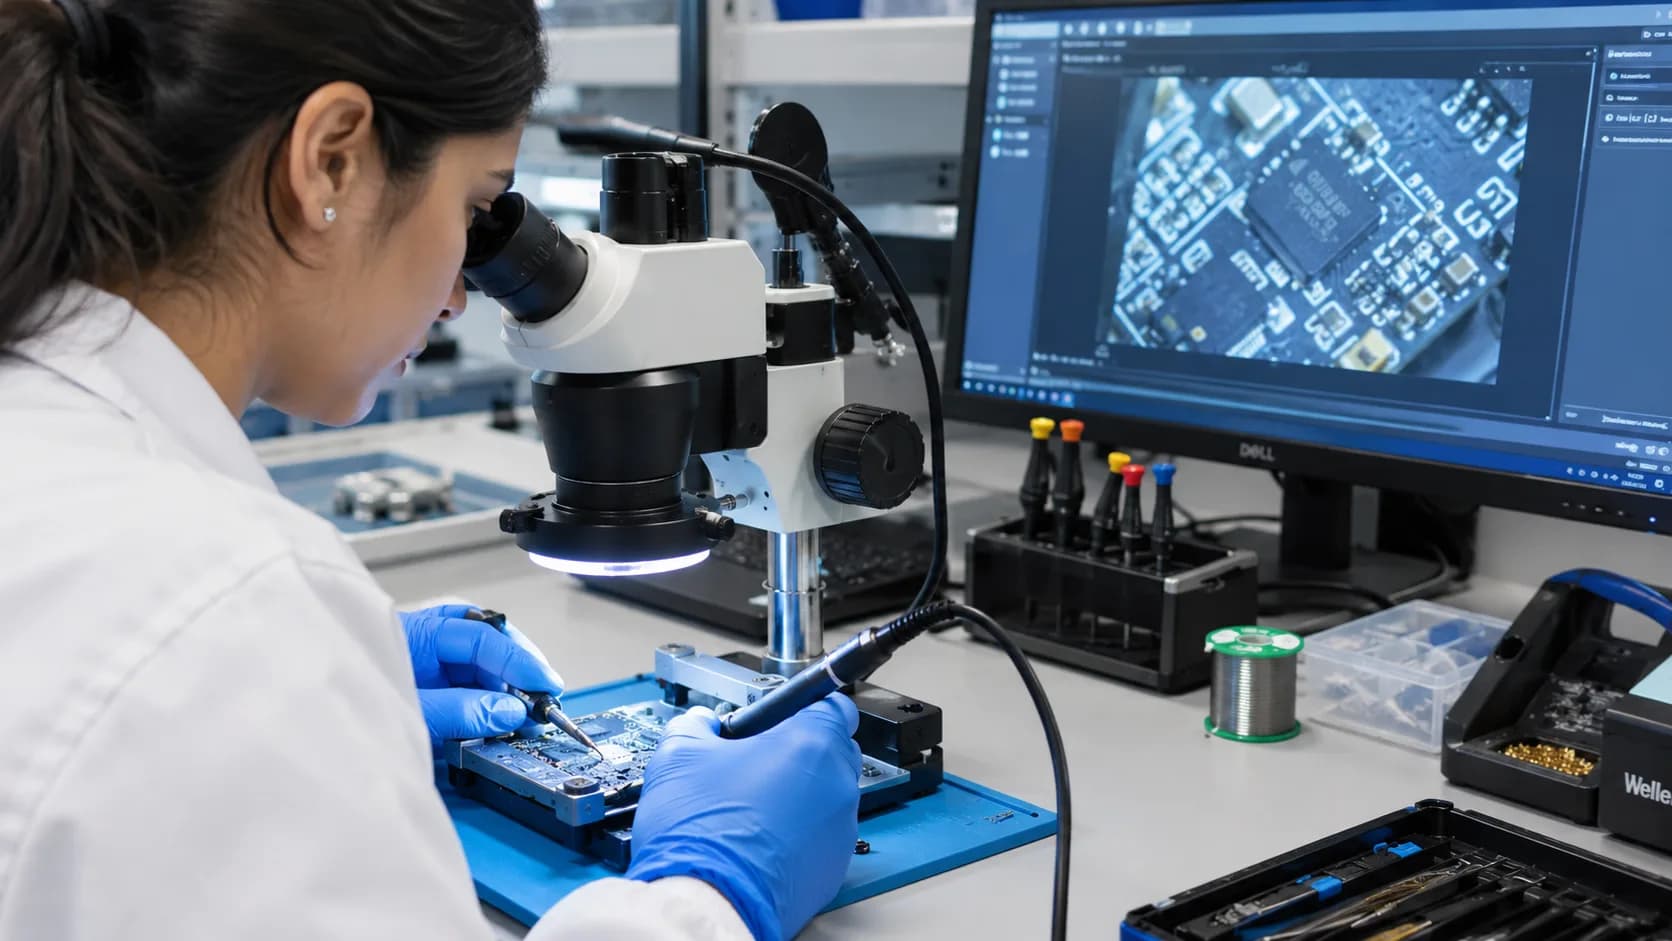
Chip-Off NAND Flash Forensics on Severely Damaged Hardware
When physical devices suffer severe physical destruction—fire damage, water submersion, intentional PCB drilling, or extreme blunt trauma—conventional software-based forensic acquisition is impossible. This technical study explores micro-soldering, direct NAND reading, and flash translation layer (FTL) algorithmic reconstruction.